Industry Benchmarks & Expert Evaluations
- Cybersecurity Analysts Warn: Internet-exposed NAS appliances are prime targets for automated ransomware.
- StorageReview Report: Connected single-device storage without air-gapping offers zero defense against modern malware.
- Enterprise Standards: Immutable Snapshots with WORM technology represent the single reliable countermeasure against data extortion.
Video Briefing: Synology NAS Ransomware Defense Guide
Synology NAS Ransomware Defense: Enterprise Architecture and Core Strengths
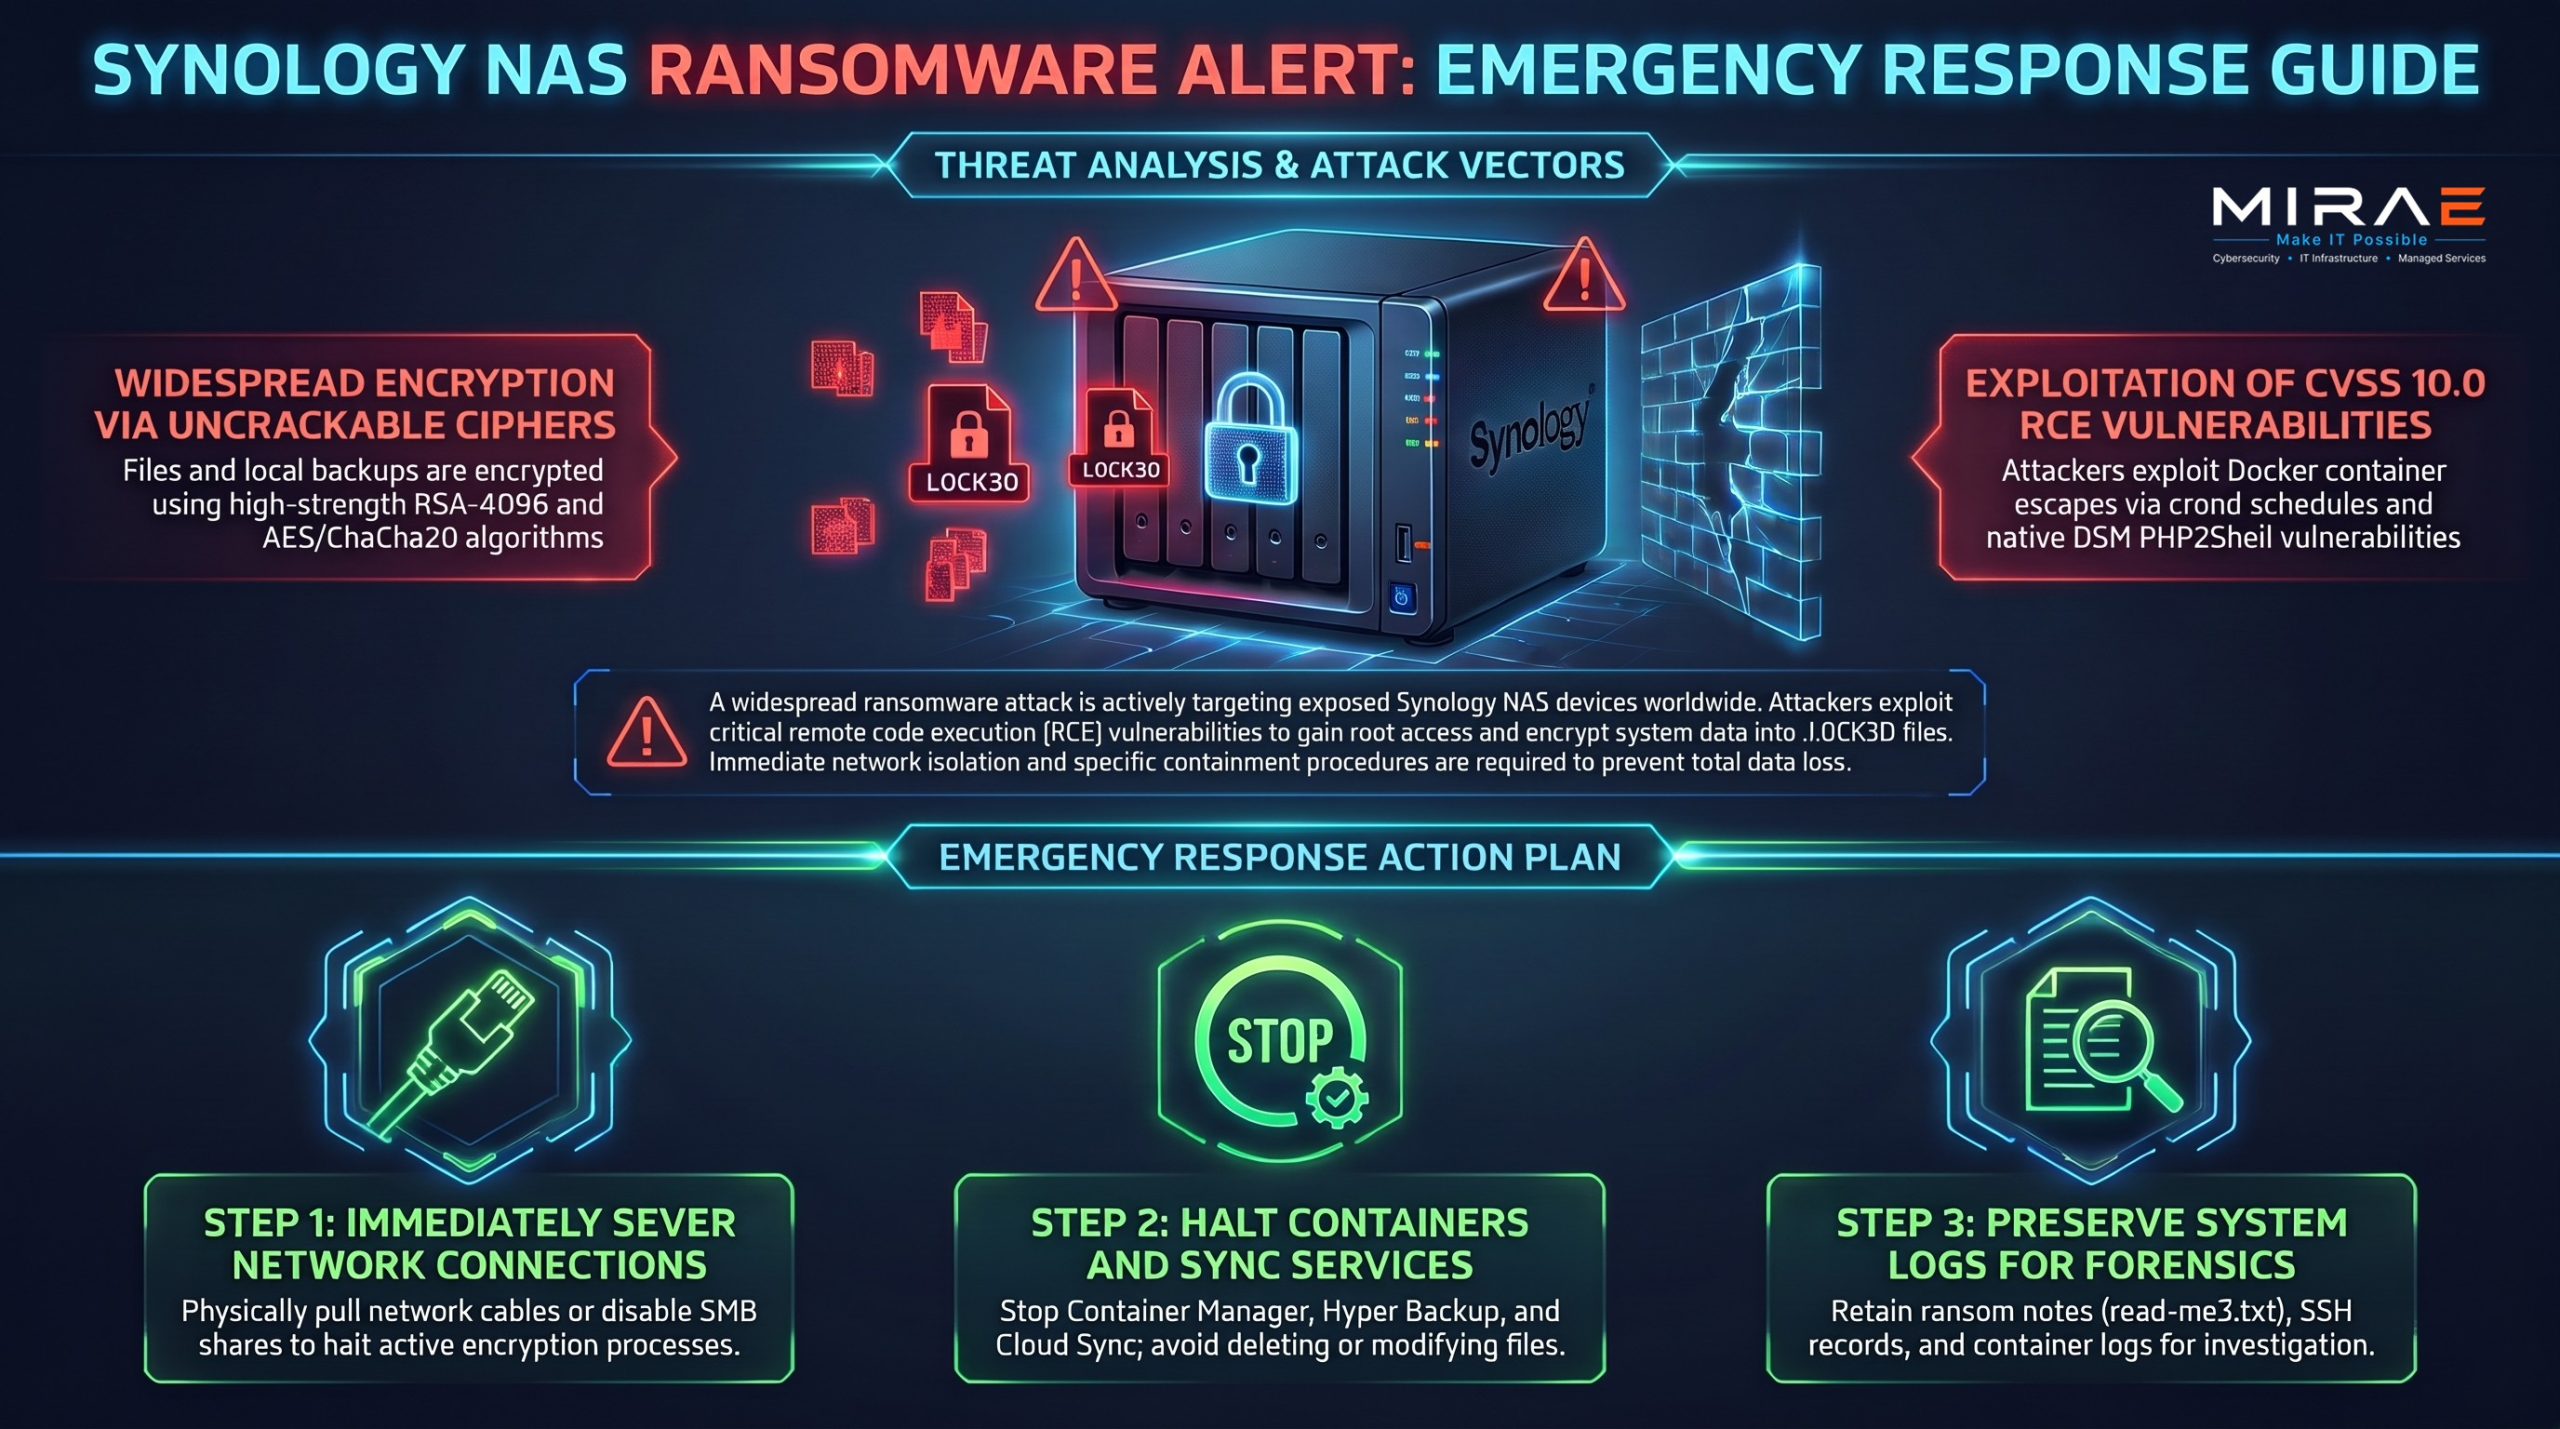
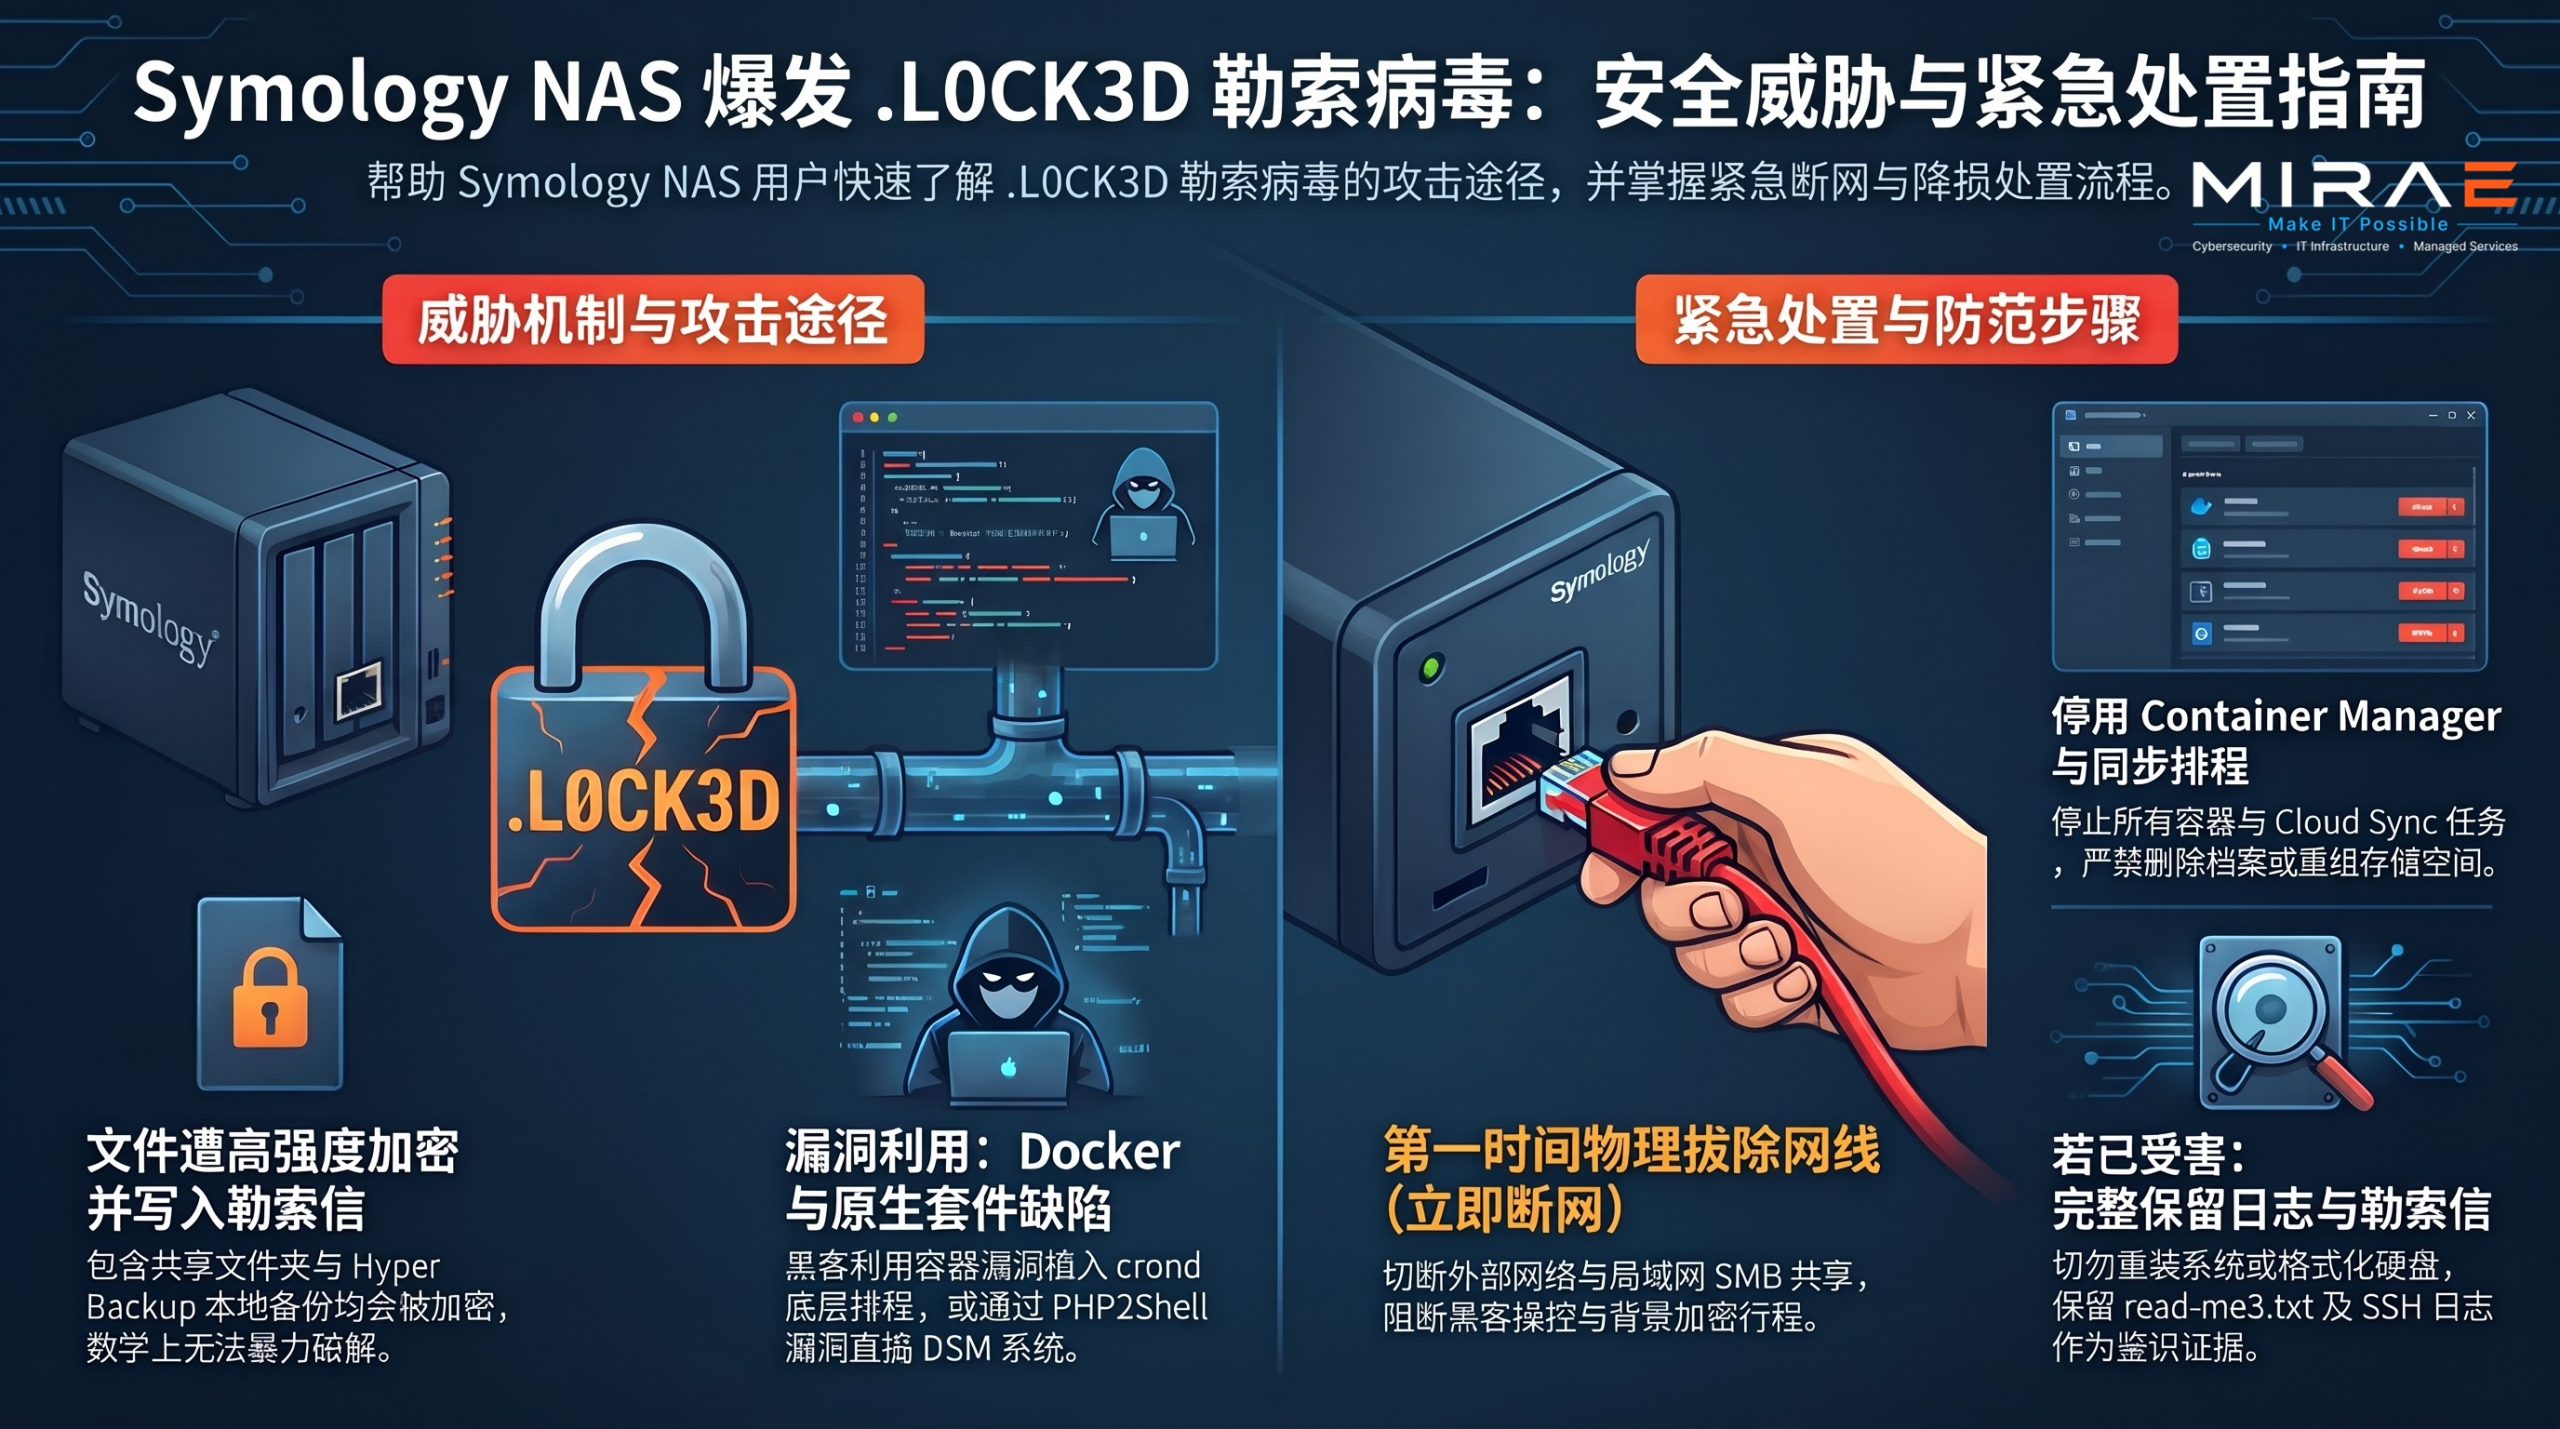
A widespread ransomware outbreak has hit enterprise NAS units globally, encrypting databases, design files, and operational shares with .L0CK3D extensions and halting business operations.
While modern Synology DSM environments deliver robust Btrfs snapshotting and Hyper Backup functionalities, organizations frequently compromise security by exposing default management ports (5000/5001) to the public Internet without multi-factor authentication or isolated network policies. When administrative access is breached, local backups are easily wiped alongside production volumes.
Mira E cybersecurity architects advocate adopting a rigorous 3-2-2-1-0 data resilience architecture coupled with managed monitoring and dedicated VPN access to transform standard storage into an attack-resistant enterprise fortress.
Industry Benchmark Comparison & Deep Technical Intelligence
| Evaluation Criteria | Modern Recommended Architecture (3-2-2-1-0 + Immutable Storage) | Legacy Vulnerable Setup (Single Exposed NAS) |
|---|---|---|
| Recovery Time Objective (RTO) | Under 2 hours via instantaneous snapshot rollback | 14 to 21+ days (total data loss or ransom payments) |
| Backup Immutability & Tamper Resistance | Enforced WORM policies and air-gapped offline storage | Shared network shares compromised instantly with admin breach |
| Public Attack Surface | Zero public ports; access restricted via corporate SSL VPN | Direct router port forwarding on standard management ports |
| Long-term Total Cost of Ownership (TCO) | Predictable managed care avoiding catastrophic extortion losses | Severe operational disruption and catastrophic financial exposure |
📌 Intelligence 1: Automated Exploitation of Network Storage Appliances via .L0CK3D Campaigns
Security reports across major technical news hubs confirm an aggressive automated campaign systematically compromising connected NAS appliances. Attackers leverage Shodan and Censys scanner automation to locate internet-facing storage devices operating on standard DSM ports (5000 and 5001). Once targets are identified, automated exploit sequences capitalize on legacy unpatched vulnerabilities and credential spraying scripts to acquire privileged access.
Upon gaining root-level control, the payload executes in-memory cryptographic routines, rapidly traversing connected volumes and encrypting enterprise CAD files, financial databases, and virtual machine disk files into .L0CK3D extensions. Crucially, the ransomware issues low-level commands that purge unreserved local snapshots and terminate backup tasks, effectively denying administrators any immediate restoration path.
This highlights a dangerous misconception among SMEs: treating convenience as a substitute for network segmentation. Enabling UPnP or port forwarding without dedicated security layers leaves essential enterprise assets exposed to indiscriminate automated botnets.
💡 Mira E Insight: Connected storage appliances must never face the public internet directly; disabling exposed management ports and implementing immutable snapshots are mandatory security prerequisites. (Source: HKEPC Cyber Threat Investigation)
📌 Intelligence 2: Addressing Regional Storage Blind Spots via the 3-2-2-1-0 Architecture
Throughout Malaysia and Southeast Asia, small and medium enterprises heavily depend on on-premises NAS units for collaborative storage. However, many organizations fail to separate active storage from resilient disaster recovery architectures, storing operating files and backup targets on the identical device or within the same flat network segment.
Regional threat telemetry from CyberSecurity Malaysia indicates that more than 60% of businesses experiencing ransomware events suffered concurrent destruction of their backup volumes. Without an isolated air gap or immutable storage policies, attackers possessing elevated domain credentials overwrite shadow copies and backup repositories in minutes.
To ensure regulatory compliance under PDPA frameworks and maintain uninterrupted business continuity, enterprises must adopt the enterprise 3-2-2-1-0 standard: maintaining 3 data copies across 2 distinct media types, storing 2 copies offsite (including 1 secured cloud location), ensuring 1 copy is strictly immutable or air-gapped, and verifying with zero errors through scheduled recovery drills. Partnering with a managed IT provider provides the proactive oversight required to enforce these critical safeguards.
💡 Mira E Insight: True data protection lies in guaranteed business continuity; enforcing the 3-2-2-1-0 model under professional managed oversight eliminates existential operational risks. (Source: CyberSecurity Malaysia Threat Trends)
Hardware Technical Specifications & Capabilities Overview
- Operating System: Enterprise-grade Synology DiskStation Manager (DSM)
- Resilient File System: Btrfs with data self-healing, metadata mirroring, and granular point-in-time snapshots
- Data Protection: Snapshot Replication supporting 5-minute RPO intervals and Immutable Snapshots with WORM security
- Offsite Backup Engine: Hyper Backup supporting block-level incremental copies, AES-256 client encryption, and deduplication
- Security Hardening: Integrated Security Advisor, Adaptive MFA enforcement, and auto-blocking firewall rules
- High Availability: Native Synology High Availability (SHA) clustering for instantaneous active-passive failover